

VPN Connectivity
VPN access routes your local machine directly into a deployment’s internal network. Once connected, your machine appears as a node on the same network as the VMs. You can reach them by IP, run local tools against them, and interact with services as if you were on-prem.
This is an advanced access method. Most users don’t need it, because the browser console gives you everything you need to operate within the lab. VPN is for when you want to bring your own toolset to bear against the environment.
Use Cases
Section titled “Use Cases”- Bring your own attacker box: VPN your local Kali (or any attack image you’ve built and tuned over years) into the scenario and engage the lab VMs like an on-prem engagement
- Running Burp Suite, Ghidra, BloodHound, Impacket, or any tool from your local machine against lab targets
- Writing and executing scripts that interact with multiple machines in the scenario network
- Connecting tools that don’t have a browser-based interface
- Anything that requires a direct network connection rather than a console session
Setting Up
Section titled “Setting Up”Click the key icon in the deployment dock to open VPN Configuration.
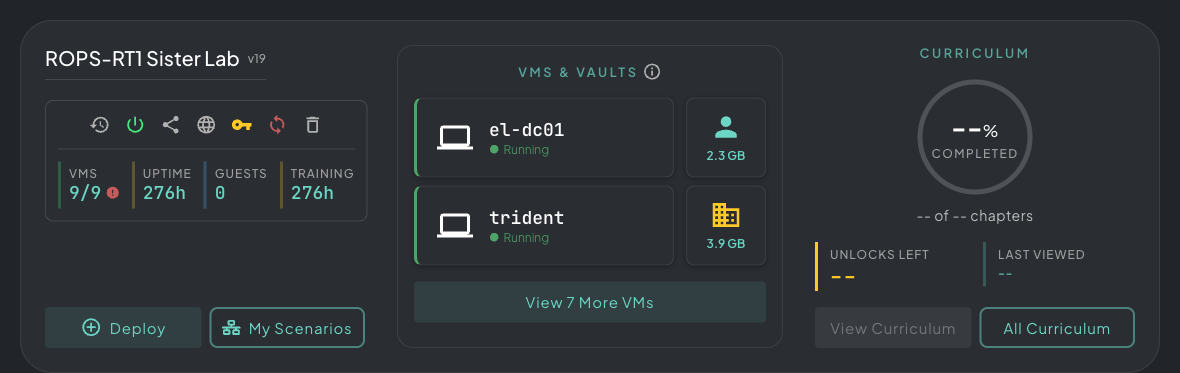 The key icon lives in the deployment dock alongside your featured VMs. Click it to open VPN Configuration.
Then click + Create Config to generate a new VPN config for this deployment.
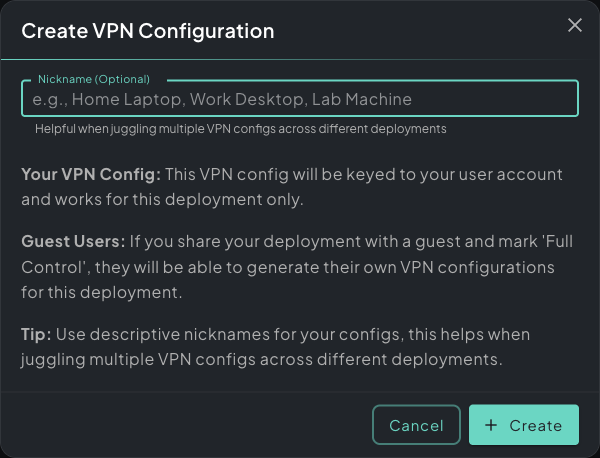 The Create VPN Configuration dialog. Each config is keyed to your user and scoped to this deployment only.
Give it a nickname, which helps if you connect from multiple machines (for example “Home Laptop” or “Work Desktop”). Each config is keyed to your user account and scoped to this deployment only. Teammates you share the lab with can generate their own separate configs if you gave them Can control host/root VMs.
The config is created in the background with a progress indicator, and the first one for a deployment can take a few minutes because it also sets up the deployment’s VPN gateway.
Once generated, the config appears in the list with a Download VPN Config button. The dialog’s Active Sessions tab lists open VPN sessions; turn on Show past sessions to include earlier ones.
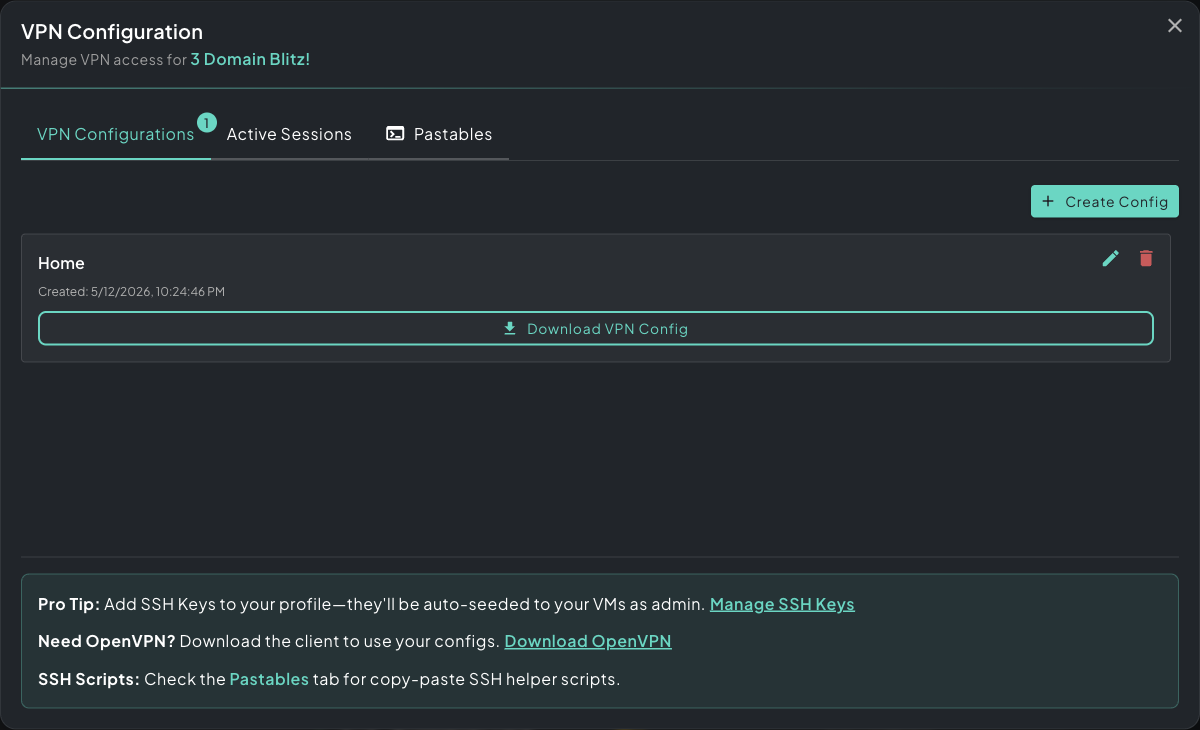 The VPN Configuration panel. Your generated config is ready to download as an .ovpn file.
Connecting
Section titled “Connecting”- Download the
.ovpnconfig file. - Import it into your OpenVPN client. Download OpenVPN if you don’t have it.
- Toggle the connection on.
Your local machine is now on the deployment’s network. Lab machines are reachable at their assigned IP addresses, visible in the deployment panel.
Firewall Reach
Section titled “Firewall Reach”When you connect over VPN, allow-all inbound rules are installed for your tunnel. Your local machine can reach any VM in the deployment on any port, regardless of the scenario’s internal firewall layout. The scenario’s own segmentation (firewalls between VLANs, AD trust boundaries, and so on) still applies to lab-to-lab traffic. It does not apply to traffic coming from you.
Think of the VPN tunnel as an admin position outside the game. It is useful for testing or scripting, but be aware that it skips the normal pathing students would take inside the scenario.
Multiple Configs
Section titled “Multiple Configs”You can create multiple configs per deployment, one per device you work from. Each config is independent, so delete ones you no longer need. If you’re running multiple concurrent deployments, each one has its own set of configs.
Disconnecting
Section titled “Disconnecting”Toggle the connection off in your OpenVPN client, or delete the tunnel. The deployment and its machines are unaffected.